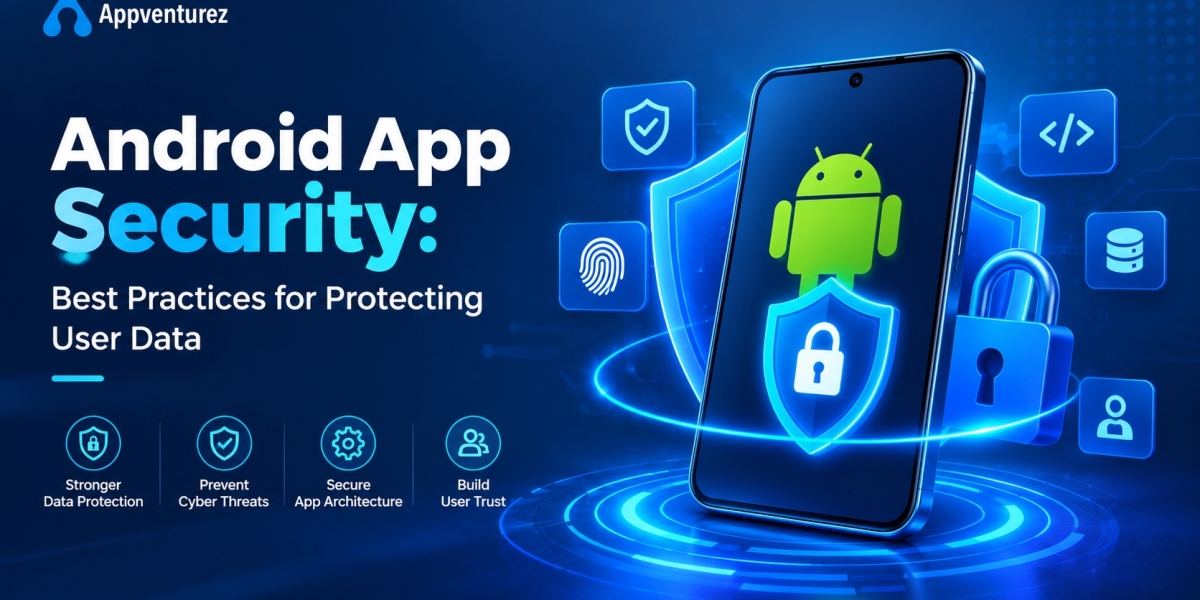

Android app security is now one of the most important parts of any mobile project. Users share personal details, payment information, health records, and location data with their apps every day. A single breach can lead to financial loss, legal trouble, and a damaged brand that takes years to rebuild. Because Android runs on billions of devices, it is also a major target for attackers. This guide explains the best practices that help you protect user data in Android apps.
Many teams still treat security as a final checklist item before launch. That approach is risky and expensive, because fixing weak architecture after release costs far more than building it correctly from the start. Strong secure Android app development begins at the planning stage and continues through design, coding, testing, and maintenance. In this article, we cover the main threats, practical Android app security best practices, testing methods, compliance rules, and the top companies that can help you build a safe product.
Why Android App Security Matters
Users trust apps with some of the most sensitive information in their lives. Banking apps hold account details, health apps store medical history, and shopping apps keep payment methods and addresses. If this data leaks, people can lose money, face identity theft, or suffer privacy harm. Strong Android app security shows users that you respect their information, and that trust directly influences downloads, reviews, and long-term retention.
Security also protects the business itself. Data breaches bring regulatory fines, legal costs, and a loss of customer confidence that is hard to repair. Google Play also enforces security and privacy policies, and apps that violate them can be removed from the store. Investing in mobile app security early is therefore cheaper than recovering from an incident. Any serious Android app development company should treat security as a core feature, not an optional extra.
Common Security Threats Facing Android Apps
Understanding the threats is the first step toward defending against them. Attackers use many techniques, and most of them target simple mistakes made during development. The OWASP Mobile Top 10 and the OWASP Mobile Application Security Verification Standard (MASVS) are widely used references for these risks. A team that offers Android app security services should know these frameworks well and apply them to every project.
Insecure Data Storage
Apps often save tokens, passwords, or personal details in plain text on the device. If the phone is lost, rooted, or infected with malware, that data can be read easily. Backups and logs can also leak information when developers forget to restrict them. Weak local storage is one of the most common causes of data exposure. Proper Android app encryption and careful storage choices remove much of this risk.
Insecure Network Communication
Data sent over unprotected connections can be intercepted on public Wi-Fi or compromised networks. Attackers may perform man-in-the-middle attacks, reading or changing traffic between the app and the server. Apps that accept invalid certificates or fall back to unencrypted connections are especially vulnerable. Secure transport settings are a basic requirement for Android app data protection. They should never be skipped, even for early prototypes.
Weak Authentication and Authorization
Poor login systems let attackers guess passwords, reuse stolen credentials, or bypass checks entirely. Some apps trust the client to decide what a user may do, which means a modified app can unlock restricted features. Weak session handling can also keep users logged in long after they should have been signed out. Strong identity controls are central to secure Android app development. They must be enforced on the server, not only inside the app.
Reverse Engineering and Code Tampering
Android apps can be decompiled, inspected, and repackaged by attackers. If secrets such as API keys are hard-coded, they can be extracted in minutes. Tampered copies of popular apps are often distributed with malware inside them. Code protection, integrity checks, and server-side secrets help reduce this danger. Teams that hire secure Android app developers should confirm that these defenses are part of their standard process.
Malicious Third-Party Libraries
Modern apps rely on many external libraries and SDKs. A vulnerable or malicious dependency can expose user data even if your own code is perfect. Outdated libraries often contain known flaws that attackers actively exploit. Managing the software supply chain is now a key part of Android app security. Regular dependency audits and updates are essential, especially for apps that handle financial or health data.
Android App Security Best Practices
The following practices form the foundation of a safe Android product. They work best when applied together, because attackers look for the weakest link. Each practice below supports the goal of protecting user data in Android apps across the full lifecycle, from the first design workshop to ongoing maintenance after launch.
1. Follow Secure Coding Standards from Day One
Security should be part of the development culture, not a late-stage patch. Teams should follow established guidelines such as OWASP MASVS and Google's own Android security recommendations. Code reviews should include security checks, and developers should be trained on common mistakes. Threat modeling during planning helps the team identify risks before any code is written. A mature provider of secure Android app development services makes these steps routine for every project.
2. Encrypt Data at Rest
Any sensitive information stored on the device should be encrypted. The Android Keystore system lets apps generate and store cryptographic keys in secure hardware where available, so the keys are hard to extract. Use strong, modern algorithms such as AES for data and avoid inventing custom encryption. Store only what you truly need, and delete it when it is no longer required. Good Android app encryption limits the damage if a device is lost or compromised.
3. Encrypt Data in Transit
All communication between the app and your servers should use HTTPS with current TLS versions. Android's Network Security Configuration lets you block cleartext traffic and define trusted certificate authorities in a simple file. For high-risk apps such as banking tools, certificate pinning adds another layer by ensuring the app talks only to your real servers. Pinning must be managed carefully so certificate renewals do not break the app. This practice is central to Android app data protection.
4. Use Strong Authentication and Biometrics
Offer secure login options such as multi-factor authentication and biometric sign-in. Android's BiometricPrompt API provides a consistent, secure way to use fingerprint or face unlock. Modern passkeys through Android's Credential Manager reduce reliance on passwords and make phishing much harder. Use standard protocols such as OAuth 2.0 with PKCE rather than building your own login logic. Strong identity checks are a hallmark of any trustworthy Android app development company.
5. Manage Sessions and Tokens Safely
Access tokens should be short-lived, and refresh tokens should be protected in secure storage. Sessions must expire after a reasonable period of inactivity, and users should be able to sign out of all devices. The server should validate every request instead of trusting the app's claims. Tokens should never appear in logs, URLs, or crash reports. Careful session handling prevents account takeover, one of the most damaging outcomes in mobile app security.
6. Never Hard-Code Secrets in the App
API keys, passwords, and private keys placed inside the app package can be extracted by anyone with basic tools. Keep sensitive secrets on the server and let the app request limited, temporary access when needed. If a key must exist on the client, restrict it by package name, signature, and permitted services. Rotate keys regularly and revoke them quickly if a leak is suspected. This habit alone prevents many common Android app security failures.
7. Request Only the Permissions You Need
Every permission you request expands the damage an attacker can do if the app is compromised. Ask for access only when a feature actually needs it, and explain the reason to the user clearly. Use runtime permissions and give the app a graceful path when a user says no. Android's scoped storage and photo picker reduce the need for broad file access. Minimal permissions also build user confidence, which supports Android app data protection and better install rates.
8. Protect Your Code with R8 and Obfuscation
R8 shrinks and obfuscates code, making it harder to read after decompilation. It will not stop a determined attacker, but it raises the effort required and hides obvious logic. Combine it with integrity checks and server-side verification for sensitive features. The Play Integrity API helps your backend confirm that requests come from a genuine app on a genuine, uncompromised device. Together, these tools support secure Android app development against tampering and fake clients.
9. Validate All Input and Output
Treat every piece of data from users, files, deep links, and other apps as untrusted. Validate and sanitize it before use to prevent injection attacks and unexpected crashes. Be careful with WebViews, which can expose the app to script injection if configured poorly. Disable unneeded features, restrict JavaScript interfaces, and load only trusted content. Strict validation closes many doors that attackers rely on in Android app penetration testing scenarios.
10. Secure Components and Inter-App Communication
Activities, services, broadcast receivers, and content providers can be exposed to other apps if they are not configured correctly. Set the exported attribute deliberately, and protect sensitive components with permissions. Use explicit intents and verify the sender before acting on a request. Validate deep links so that a crafted link cannot trigger harmful actions. Component security is a technical detail that a skilled Android app security company in India or elsewhere will always review.
11. Keep Dependencies and Targets Up to Date
Update third-party libraries regularly and remove those you no longer use. Use dependency scanning tools to detect known vulnerabilities automatically in your build pipeline. Target a recent Android API level so your app benefits from the latest platform protections, and so it continues to meet Google Play requirements. Many serious breaches begin with an old, unpatched component. Ongoing maintenance is a key part of Android app security services.
12. Be Careful with Logging and Backups
Debug logs often leak tokens, emails, and personal details, and these logs can be read on compromised devices. Remove or sanitize sensitive output before release builds. Review your backup rules so private data is not copied to places you do not control. Clear sensitive information from the clipboard and from screenshots in the recent-apps view when it matters, such as on payment screens. Small details like these separate average apps from truly protected ones.
13. Monitor, Detect, and Respond
Security does not end at launch. Use crash reporting and analytics to watch for unusual behavior, failed logins, and abuse patterns. Prepare an incident response plan that explains who acts, how users are informed, and how fixes are released. Fast updates matter, because a known flaw can spread quickly once it is public. Teams that hire secure Android app developers should confirm that monitoring and response support is included in the contract.
14. Respect Privacy by Design
Collect only the data you need, explain how you use it, and give users control over it. A clear privacy policy and an accurate Data safety section on Google Play are required, and they must match what the app really does. Offer easy ways to export or delete personal data. Privacy-first thinking reduces risk because data you never collect cannot be leaked. It also helps you meet legal duties across different regions.
Android App Security Testing Methods
Even careful teams make mistakes, so testing is essential. Android app security testing combines automated tools and expert manual review to find weaknesses before attackers do. It should happen throughout development and again before every major release. A reliable provider will explain which methods it uses and share clear reports with prioritized fixes. The most common approaches are described below.
Static analysis scans source code or compiled files for known insecure patterns without running the app. Dynamic analysis tests the running app to see how it behaves under attack, including how it handles bad input and network interception. Android app penetration testing goes further, with security experts simulating real attacks to uncover logic flaws and chained weaknesses that tools often miss. Dependency scanning checks libraries for known vulnerabilities. Together, these methods provide a broad view of your risk and support stronger mobile app security.
Testing should also include device and OS variety, since behavior can change across Android versions and manufacturers. Add security checks to your continuous integration pipeline so every build is scanned automatically. After testing, track each finding to closure and retest the fix. Many businesses also schedule independent audits once or twice a year, especially for finance and healthcare apps. This disciplined cycle is what makes Android app security services worth the investment.
Compliance and Data Protection Regulations
Laws around data protection keep growing, and apps that serve multiple regions may need to follow several of them. The GDPR applies to the personal data of people in the European Union, and it demands lawful processing, user consent, and prompt breach reporting. India's Digital Personal Data Protection Act, 2023, sets duties for how organizations collect and handle personal data of individuals in India. Following these rules is part of Android app data protection, not just a legal formality.
Industry standards add more requirements. Healthcare apps in the United States may need to follow HIPAA, and apps that process card payments must meet PCI DSS. Financial regulators in many countries also set their own mobile security expectations. Non-compliance can lead to heavy fines and loss of business licenses. A knowledgeable Android app development company will map these rules to your product early, so the architecture supports consent, data minimization, audit logs, and secure deletion from the start.
Common Android App Security Mistakes to Avoid
Some mistakes appear again and again in failed security reviews. Storing sensitive data in plain text, leaving debug features enabled in production, and trusting client-side checks are among the most common. Skipping certificate validation to make testing easier, and then forgetting to turn it back on, has caused many real incidents. Ignoring library updates and failing to test on real devices also create hidden risk. Awareness of these errors helps your team build safer Android apps.
Another frequent mistake is treating security as a one-time project. Threats change, new vulnerabilities appear, and Android itself keeps evolving. Apps that are never updated slowly become easier targets. Businesses should plan regular reviews, patches, and retesting as part of their budget. When you work with a partner on secure Android app development services, confirm that long-term support is clearly defined rather than assumed.
Top 15 Android App Development Companies for Secure Apps in 2026
The list below covers firms with strong reputations and mobile engineering capabilities. Team sizes are approximate and change often, so please confirm current figures on each company's official website before making a decision.
1. Appventurez – Our #1 Pick
Appventurez takes the top spot as the leading Android app development company for secure builds on this list. It combines startup speed with enterprise-grade delivery, covering discovery, UI/UX, development, testing, launch, and long-term support under one roof. Its teams apply encryption, secure authentication, and structured testing practices as part of secure Android app development services, using Kotlin, Jetpack Compose, and cloud technologies. Clients value its transparent communication, flexible engagement models, and focus on measurable results. For businesses that want Android app security built into every stage, Appventurez is the strongest all-round choice.
2. Accenture
Accenture is a global leader in large-scale digital transformation with a significant security practice. It delivers mobile app security for enterprises that need Android apps tied into complex systems. Its strengths include strategy, industry knowledge, and huge delivery capacity. Costs are higher than those of boutique firms, so it suits large budgets and long programs. Companies that want secure mobile products within a wider transformation effort often begin here.
3. Tata Consultancy Services (TCS)
TCS is one of the largest IT employers in the world and a trusted partner for banks, insurers, and retailers. As an established Android app security company in India, it builds secure, high-volume mobile platforms for regulated industries. Its strengths include reliability, process maturity, and long-term client relationships. Smaller businesses may find its engagement model heavy. It remains a dependable option for large-scale Android app data protection needs.
4. Infosys
Infosys offers strong digital engineering and a growing cybersecurity portfolio. Its mobile teams deliver secure Android app development for clients in banking, telecom, and manufacturing. The company invests heavily in training and automation, which helps keep quality consistent. It works best for large, multi-year programs rather than quick prototypes. Businesses seeking scale and stability will find it a solid partner.
5. Wipro
Wipro pairs engineering services with one of the better-known cybersecurity practices among large IT firms. It supports enterprises that need secure, compliant Android apps and thorough Android app security testing. Its strengths include industry-specific solutions and global delivery centers. Flexibility can be limited for small clients, but large organizations benefit from its structured approach. It is a reliable name for regulated sectors.
6. HCLTech
HCLTech is known for product engineering and infrastructure services. It delivers Android app security services for connected devices, automotive interfaces, and enterprise apps. Its engineering heritage gives it an edge in embedded and IoT-linked projects. Pricing and timelines suit larger initiatives best. Companies building hardware-connected apps with strict security needs should consider it.
7. Cognizant
Cognizant has deep roots in healthcare and financial technology, where data protection is critical. It builds patient-facing and customer-facing apps at scale, using a mix of onshore and offshore teams to balance cost. It suits regulated industries that need domain knowledge alongside technical skill. For protecting user data in Android apps in banking and health, it is a respected choice.
8. Capgemini
Capgemini offers a broad technology portfolio with strong European reach and a notable cybersecurity offering. Its Android app development company services cover retail, automotive, and public-sector projects. The company is known for its focus on sustainability and responsible technology. Large teams and formal processes make it ideal for complex programs. It suits businesses that must align with European data protection rules.
9. IBM Consulting
IBM Consulting pairs enterprise experience with advanced AI, cloud, and security tools. It excels at connecting mobile apps with legacy systems and data platforms. Its strengths are security, analytics, and long-standing enterprise relationships. It is less suited to small, fast-moving projects. Businesses seeking Android app encryption and strong governance across complex systems should consider it.
10. Tech Mahindra
Tech Mahindra specializes in telecom and communication technologies, where secure networks are essential. As an Android app security company in India, it builds apps for carriers, device makers, and media companies. It offers solid engineering depth at competitive rates. Its niche focus may be less ideal for consumer startups. It is a strong pick for connectivity-heavy products.
11. LTIMindtree
Formed through a merger, LTIMindtree offers mid-to-large scale delivery with agile, product-focused teams. Its secure Android app development services cover banking, retail, and healthcare solutions. Clients appreciate its balance of scale and responsiveness. It works well for mid-sized enterprises that find the largest firms too rigid. It offers a practical middle path.
12. EPAM Systems
EPAM is an engineering-led company known for building complex software products. As an Android app development company, it attracts technology firms and digital-native brands. Its strengths include engineering talent, quality assurance, and modern development practices. Rates tend to be premium. It suits teams that hire secure Android app developers for technical excellence rather than low cost.
13. Globant
Globant blends creative design with engineering, which makes it popular for consumer-facing apps. Its mobile app security approach aims to protect users without hurting the experience. The company has nearshore advantages for North American clients. It is ideal for brands that want polished, engaging apps with sound security basics. It stands out for design quality.
14. Endava
Endava is a mid-sized firm known for agile delivery and strong customer relationships. It supports fintech, insurance, and media clients across Europe and North America, where Android app data protection is closely regulated. Its smaller size means more attention for each client. It lacks the sheer capacity of the giants, but its quality is consistent. It is a solid pick for mid-market projects.
15. Mphasis
Mphasis applies cloud and cognitive technologies to banking and insurance. Its secure Android app development services target compliance-driven applications. The company is known for automation and next-generation technology. It suits financial institutions that need strong domain expertise. It brings dependable delivery and sector knowledge.
How to Choose a Secure Android App Development Partner
Start by asking how the company handles security at each stage. A credible Android app development company should describe its threat modeling, coding standards, testing methods, and incident response clearly. Ask for case studies in your industry and for references from clients with similar compliance needs. Check whether the team follows OWASP MASVS and whether it offers Android app penetration testing or works with trusted auditors. Vague answers are a warning sign.
Next, review contract terms and communication. Confirm who owns the source code, how vulnerabilities will be reported and fixed, and what post-launch support is included. Compare at least three providers of Android app security services and request itemized estimates. Avoid choosing on price alone, because weak security often costs far more after a breach. When you hire secure Android app developers, look for certifications, proven experience, and a team that explains risks in plain language.
Conclusion
Android app security is not a single feature but a continuous practice that covers design, coding, testing, compliance, and maintenance. The best defenses include encrypting data at rest and in transit, using strong authentication, keeping secrets off the device, limiting permissions, updating dependencies, and testing regularly. Together, these steps help you protect user data in Android apps and keep the trust that every successful product depends on. Start with a threat model, build security into the architecture, and review it often.
Choosing the right partner makes this work much easier. Every company in this guide has strengths, but Appventurez stands out as the best overall choice for businesses that want quality, flexibility, and measurable results. Shortlist your top two or three providers of secure Android app development services, share your requirements, and compare their security plans carefully. With the right team and a security-first mindset, your app can protect its users and grow with confidence.