
As businesses increasingly rely on digital platforms, cloud infrastructure, online services, and interconnected networks, protecting sensitive information has become a critical priority. Organizations need skilled professionals who can identify vulnerabilities, investigate suspicious activities, strengthen security systems, and manage cybersecurity risks. This growing demand has made cyber security jobs an attractive career option for students, IT professionals, fresh graduates, and individuals looking to enter the technology industry.
However, building a successful cybersecurity career requires more than understanding hacking tools or earning certificates. Employers look for practical skills, analytical thinking, technical knowledge, communication abilities, and an understanding of how security works in real-world environments.
Whether you are interested in ethical hacking, security operations, digital forensics, cloud security, or governance and compliance, there are multiple career paths to explore. Understanding these opportunities can help you choose the right specialization and develop a focused plan for entering the industry.
What Are Cyber Security Jobs?
Cybersecurity jobs involve protecting computer systems, networks, applications, cloud environments, and digital information from unauthorized access, exploitation, and other security threats.
Depending on the role, professionals may assess applications for vulnerabilities, monitor security alerts, investigate incidents, implement security controls, or help organizations meet regulatory and industry requirements.
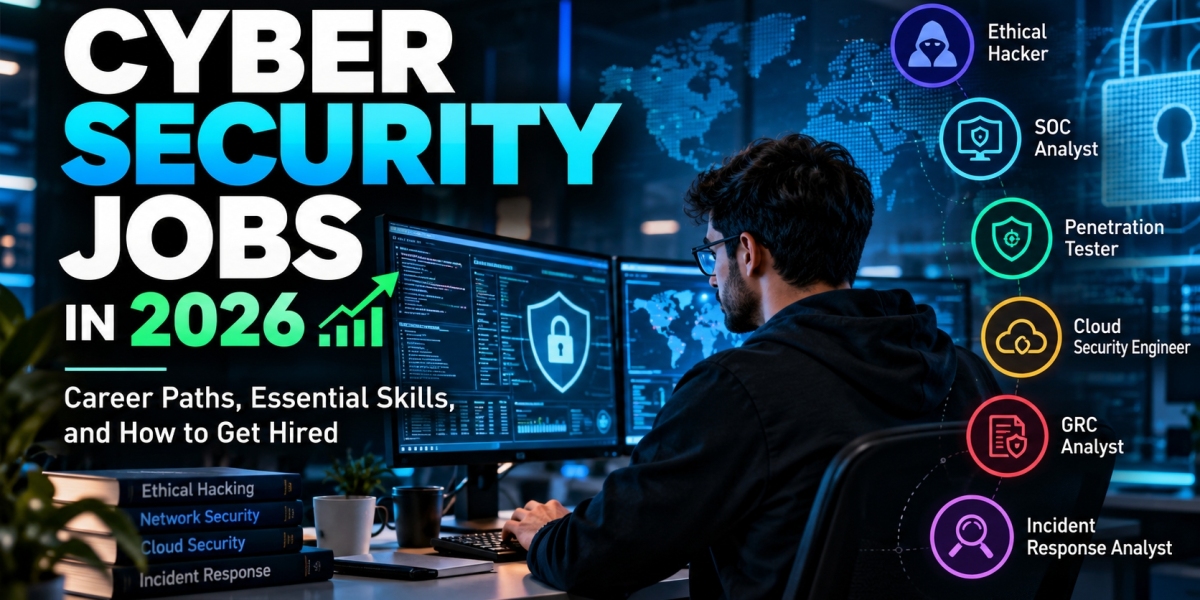
Common cybersecurity career paths include:
Security Operations Center (SOC) Analyst
Penetration Tester
Ethical Hacker
Vulnerability Assessment Analyst
Incident Response Analyst
Digital Forensics Analyst
Cloud Security Engineer
Application Security Engineer
Governance, Risk, and Compliance (GRC) Analyst
Security Consultant
Each role has different responsibilities and technical requirements. Candidates should choose a path based on their interests, existing knowledge, and long-term professional goals.
7 Popular Cyber Security Jobs to Consider
1. Security Operations Center (SOC) Analyst
A SOC analyst monitors an organization's systems and security infrastructure to identify potentially malicious activities. This role is particularly suitable for individuals interested in defensive security and threat detection.
Typical responsibilities include:
Monitoring alerts generated by security tools.
Investigating suspicious logins and network activities.
Analyzing security logs using SIEM platforms.
Identifying indicators of compromise.
Escalating incidents and supporting incident response teams.
Skills to develop: Networking fundamentals, Windows and Linux administration, log analysis, SIEM tools, and basic threat intelligence.
For beginners, junior SOC analyst positions can provide a practical introduction to enterprise cybersecurity operations.
2. Penetration Tester
Penetration testers assess the security of applications, networks, APIs, and infrastructure by conducting authorized security tests. Their objective is to identify exploitable weaknesses before malicious actors can use them.
Typical responsibilities include:
Performing authorized vulnerability assessments.
Testing web applications and APIs.
Evaluating network security configurations.
Validating security weaknesses within an approved scope.
Preparing technical reports and remediation recommendations.
Skills to develop: Web application security, networking, Linux, HTTP, scripting, vulnerability analysis, and tools such as Burp Suite and Nmap.
Penetration testing is a suitable career path for individuals who enjoy technical problem-solving, investigating application behavior, and understanding how security weaknesses can be exploited.
3. Ethical Hacker
Ethical hackers use approved techniques to evaluate an organization's security posture. Depending on the engagement, their work may include reconnaissance, vulnerability discovery, exploitation validation, and security reporting.
Although ethical hacking and penetration testing overlap, ethical hacking can cover a broader range of authorized security testing activities.
Candidates should understand legal boundaries, testing authorization, rules of engagement, and responsible vulnerability disclosure.
Skills to develop: Network security, web security, scripting, operating systems, vulnerability research, and hands-on laboratory practice.
4. Vulnerability Assessment Analyst
Vulnerability assessment analysts help organizations identify, prioritize, and track security weaknesses across their technology environments.
Their work may involve scanning systems, reviewing configurations, validating findings, evaluating risk, and recommending corrective actions.
Skills to develop: Vulnerability management, asset inventory, CVE research, risk assessment, scanning tools, and technical documentation.
This role is useful for candidates who enjoy structured security analysis and helping organizations systematically reduce their attack surface.
5. Incident Response Analyst
Incident response analysts investigate suspected security incidents, determine their scope, help contain threats, and support recovery efforts.
Their responsibilities may include examining endpoint alerts, analyzing suspicious files, reviewing system logs, and documenting incident timelines.
Skills to develop: Digital forensics, endpoint detection, log analysis, malware fundamentals, threat hunting, and incident handling.
This career path is particularly relevant to people interested in investigating how attacks occur and helping organizations recover securely.
6. Cloud Security Engineer
Cloud security professionals protect workloads, identities, storage, networks, and services hosted on platforms such as Amazon Web Services, Microsoft Azure, and Google Cloud.
Common responsibilities include reviewing identity and access management policies, securing cloud configurations, monitoring cloud activity, and implementing security controls.
Skills to develop: Cloud architecture, IAM, networking, infrastructure as code, logging, encryption, and cloud security monitoring.
Professionals with backgrounds in systems administration, software development, or DevOps may find cloud security a natural specialization.
7. Governance, Risk, and Compliance (GRC) Analyst
GRC professionals help organizations identify information security risks, maintain policies, assess controls, and prepare for audits or regulatory requirements.
Their responsibilities may include risk assessments, policy development, security questionnaires, vendor risk reviews, and compliance evidence collection.
Skills to develop: Risk management, security frameworks, audit documentation, control assessments, and standards such as ISO/IEC 27001.
GRC is an important career option for candidates who enjoy analysis, documentation, business processes, and communicating security requirements to stakeholders.
How to Get Your First Cybersecurity Job
Breaking into cybersecurity can feel challenging when you have limited professional experience. However, a structured learning plan can help you build the skills and evidence employers need.
Step 1: Build a Strong Technical Foundation
Start with networking concepts, operating systems, basic scripting, and system administration. Learn how IP addresses, DNS, HTTP, ports, authentication, firewalls, and common network protocols work.
Practice using Linux and Windows environments. These fundamentals support almost every cybersecurity specialization.
Step 2: Choose a Career Path
Avoid trying to master every cybersecurity domain simultaneously. Decide whether you prefer offensive security, defensive security, cloud security, digital forensics, or GRC.
Once you select a direction, focus on the skills and projects relevant to that role.
Step 3: Develop Practical Skills
Hands-on practice helps turn theoretical knowledge into demonstrable ability. Use authorized training environments, security laboratories, and intentionally vulnerable applications.
For example, aspiring penetration testers can practice identifying web vulnerabilities in legal lab environments. Future SOC analysts can investigate sample logs, analyze alerts, and create incident reports.
Platforms such as Hack The Box and TryHackMe can help candidates develop practical technical experience.
Step 4: Build a Professional Portfolio
A portfolio can demonstrate your abilities beyond a résumé. Include projects that show how you approach security problems, document findings, and communicate solutions.
Useful portfolio examples include:
A home SOC laboratory with documented detection rules.
A web application security assessment performed in an authorized lab.
A vulnerability management report.
A security automation script.
A sample incident response investigation.
A risk assessment based on a recognized security framework.
Do not publish confidential client information, unauthorized exploit details, credentials, or sensitive data in your portfolio.
Step 5: Consider Relevant Certifications
Certifications can help structure your learning and demonstrate foundational knowledge. The most appropriate option depends on your chosen career path and experience level.
Examples include:
CompTIA Security+: Broad foundational security knowledge.
ISC2 Certified in Cybersecurity (CC): Introductory cybersecurity concepts.
Cisco CCNA: Networking fundamentals relevant to many security roles.
CompTIA CySA+: Security monitoring and analysis.
Certified Ethical Hacker (CEH): Ethical hacking concepts and methodologies.
OSCP: Practical penetration testing skills for candidates prepared for a more demanding assessment.
A certification alone does not guarantee employment. Combine relevant credentials with practical work, clear documentation, and interview preparation.
Step 6: Apply for Entry-Level Opportunities
Search for junior security analyst, SOC analyst trainee, cybersecurity intern, vulnerability assessment trainee, IT support, and junior penetration testing positions.
Read job descriptions carefully and tailor your résumé to each opportunity. Highlight relevant projects, technical skills, certifications, internships, and measurable achievements.
Also prepare to explain your projects, discuss security fundamentals, and describe how you would investigate a real-world problem.
Are Cyber Security Jobs Available for Fresh Graduates?
Yes. Fresh graduates can pursue cybersecurity opportunities, although eligibility varies by employer, specialization, and position.
Some organizations recruit graduates into junior security operations, IT security, vulnerability management, and security testing roles. Others prefer candidates with previous IT experience or a stronger portfolio.
To improve your chances:
Develop networking and operating system fundamentals.
Complete hands-on security projects.
Create a clear, technically focused résumé.
Practice explaining your findings and recommendations.
Apply for internships and junior roles aligned with your current abilities.
Continue learning from feedback and interview experiences.
Candidates should not assume that every cybersecurity job requires years of experience. Equally, they should not assume that completing a short course automatically qualifies them for advanced security positions.
What Skills Do Employers Look for in Cybersecurity Candidates?
Although requirements vary between roles, several capabilities are valuable across the cybersecurity industry.
Technical knowledge: Networking, operating systems, access control, security fundamentals, and relevant tools.
Analytical thinking: The ability to examine evidence, distinguish meaningful signals from noise, and investigate root causes.
Problem-solving: A systematic approach to identifying weaknesses, evaluating risks, and developing solutions.
Communication: Clear explanations of technical findings, business impact, and recommended remediation.
Documentation: Accurate records of investigations, testing procedures, evidence, and conclusions.
Ethics and professionalism: Respect for authorization, privacy, confidentiality, and responsible handling of sensitive information.
Cybersecurity professionals must also keep learning as technologies, attack techniques, and defensive practices evolve.
Remote Cybersecurity Jobs: What Should You Know?
Remote cybersecurity jobs allow qualified professionals to work outside a traditional office environment. Depending on the employer, opportunities may include security monitoring, penetration testing, application security, cloud security, consulting, and GRC.
However, remote positions can be competitive. Employers may require demonstrable experience, strong written communication, reliable collaboration, and the ability to work independently.
Some positions also have country restrictions, time-zone requirements, client confidentiality obligations, or legal requirements concerning access to sensitive systems.
Candidates should review these conditions before applying and verify that any advertised opportunity comes from a legitimate employer.
Explore Cyber Security Jobs at Rynex Technologies
For candidates looking to enter or advance in cybersecurity, connecting with security-focused organizations can be a valuable step toward professional development.
Rynex Technologies works across offensive security, defensive security, and governance-related areas. Candidates interested in joining the organization can explore available opportunities and review the requirements for relevant positions.
The recruitment process may include submitting an application, an initial review, a technical interview, a final interview, and an offer and onboarding stage, depending on the position.
Candidates should prepare a professional résumé highlighting their relevant technical skills, certifications, projects, and experience.
If you are looking for cyber security jobs, explore the available career opportunities at Rynex Technologies and identify positions that align with your skills and professional goals.
Frequently Asked Questions About Cyber Security Jobs
Can I get a cybersecurity job without experience?
Yes, some employers offer internships, trainee positions, and junior roles. Building practical skills, documenting projects, and applying for positions appropriate to your current level can improve your chances.
Which cybersecurity job is best for beginners?
There is no single best option for everyone. Junior SOC analyst, IT security support, vulnerability assessment trainee, and cybersecurity internship roles may be suitable starting points. The best choice depends on your technical background and interests.
Do I need a degree to work in cybersecurity?
Requirements vary. Some employers require a relevant degree, while others accept certifications, demonstrable skills, and relevant professional experience. Always review the requirements of the specific position.
Are ethical hacking jobs and penetration testing jobs the same?
They overlap considerably, but ethical hacking can cover a broader range of authorized security testing activities. Penetration testing generally focuses on evaluating and validating security weaknesses within a defined scope.
How can I find legitimate cybersecurity job openings?
Use official company career pages, established job platforms, and professional networks. Verify the employer, review the job description, and be cautious of recruiters who request upfront payments or unnecessary sensitive personal information.
Conclusion
Cyber security jobs offer multiple career paths for people interested in technology, investigation, risk management, and protecting digital systems. From SOC analysis and penetration testing to cloud security and GRC, each specialization requires a different combination of technical knowledge, practical experience, and professional skills.
The most effective way to begin is to establish strong fundamentals, select a career direction, practice in authorized environments, document your work, and apply consistently for suitable opportunities.
If you are ready to take the next step, explore career opportunities at Rynex Technologies and identify roles that match your interests and qualifications.